

Science & Tech · Cybersecurity · 2 days ago
US seizes two China-linked hacking tools used against critical infrastructure

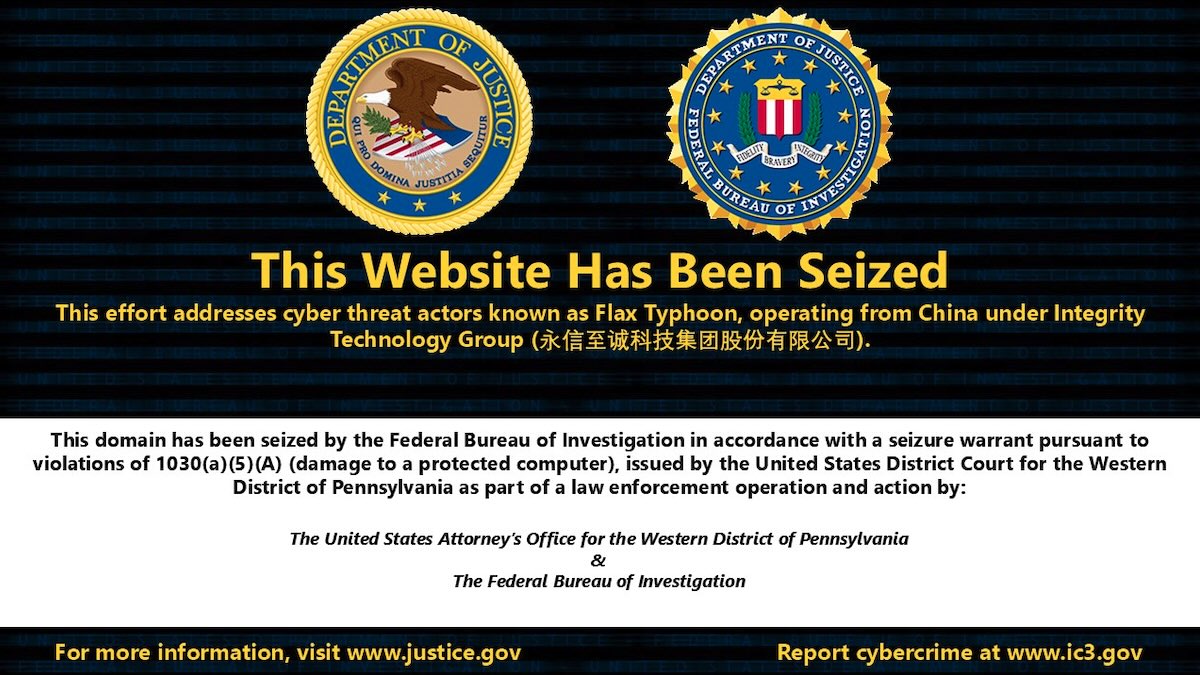
The FBI and Justice Department seized domains used to operate two hacking tools, Microscan and FishHub.
US officials link the tools to Integrity Technology Group, a China-based company with contracts with the Chinese government.
They say the company worked with hackers known as Flax Typhoon, who targeted organizations in the US and other countries.
Microscan scanned networks for software weaknesses, while FishHub used phishing emails to break into networks and install more malware.
Targets included a US power company, airports in Japan and Poland, and Taiwanese power companies and universities.
Officials say FishHub was used against about 20 Taiwanese universities, and the malware could give clients remote access or steal files.
This is the second public disruption of Integrity Tech’s infrastructure; the US disrupted a botnet linked to the company in 2024.
Government agencies have also advised organizations to patch software, enable multi-factor authentication and disable services they do not use.

The FBI and Justice Department said they seized tools called Microscan and FishHub that were used to scan and gain access to networks in the United States and other countries.
U.S. authorities link the tools to Integrity Technology Group, a China-based company they say has contracts with the Chinese government and is associated with the Flax Typhoon hacking group.
Microscan was used to scan targets including a South Carolina power company, airports in Japan and Poland, and organizations in Taiwan.
FishHub used spear-phishing to gain access to networks and could deliver malware, enable remote access or search for and send files to Integrity Tech-controlled servers.
The FBI and partner agencies issued a joint advisory describing the group’s activity and recommending measures including applying security patches and enabling multi-factor authentication.
China’s foreign ministry said the country opposes hacking and accused the United States of political manipulation.
- Who
- The FBI and Justice Department; the tools are linked by U.S. authorities to Integrity Technology Group and the Flax Typhoon hacking group.
- What
- Seizure of the Microscan and FishHub cyber tools and related domains.
- When
- Announced Thursday, October 8, 2026.
- Where
- The tools targeted networks in the United States and abroad; court-authorized seizures were granted in the Western District of Pennsylvania.
- Why
- U.S. authorities said the seizures were intended to deny hackers access to tools used to scan and intrude on networks.
U.S. authorities
China
Who is responsible for the cyber activity
U.S. authorities
U.S. authorities say Integrity Technology Group, a company with Chinese government contracts, operated the tools and enabled cyber actors linked to Flax Typhoon.
China
China’s foreign ministry said China cracks down on hacking in accordance with the law and opposes the spread of disinformation for political purposes.
How the issue should be addressed
U.S. authorities
The FBI and Justice Department said seizing the tools would disrupt the operation and make it harder to target networks and infrastructure.
China
China urged the United States to abandon what it called double standards and political manipulation, and to address cybersecurity risks through equal dialogue and consultation.
We aim to remove the capability from the threat actors. We target their infrastructure, their money, and their tools
We urge the U.S. to abandon its double standards and political manipulation, and work with China through equal dialogue and consultation to jointly address cybersecurity risks,
By exposing and disrupting these enablers, we make it harder for the PRC to target American networks and infrastructure.
These seizures, our second disruption of Integrity Tech’s massive operations in as many years, send another clear message to cybercriminals from the PRC and elsewhere of the Department’s dedication to defending and maintaining cybersecurity in the United States and abroad.
Microscan was used to scan a South Carolina power company, airports in Japan and Poland, and organizations in Taiwan.
Microscan scanned two Taiwanese universities, which attackers broke into soon afterward, according to the Justice Department.
U.S. authorities disrupted a Mirai-variant botnet associated with Integrity Tech that had infected more than 200,000 consumer devices.
The FBI and Justice Department announced seizures of Microscan, FishHub and related domains, alongside a joint cybersecurity advisory.
- Tools seized
- Microscan and FishHub
- Company linked to the tools by U.S. authorities
- Integrity Technology Group
- Microscan target locations named
- South Carolina; Japan; Poland; Taiwan
- Confirmed FishHub victims
- About 20 Taiwanese universities
- Previous botnet disruption
- September 2024; more than 200,000 consumer devices
Sources
FBI seizes Chinese hacking tools used for cyberattacks on critical U.S. infrastructure

US Disrupts China-Linked Integrity Tech ‘s Cyber Espionage Tools

FBI disrupts Flax Typhoon hacking tools used in global cyberattacks
US Disrupts Chinese State-Sponsored Hacking Tools

FBI Seizes 7 Domains, Disrupts Flax Typhoon Tools Used in Critical Infrastructure Intrusions
FBI disrupts Chinese hacking tools used to breach critical infrastructure
DOJ, FBI seize Flax Typhoon-linked hacking tools Microscan, FishHub
Related news
Canadian cybersecurity negotiator arrested in ShinyHunters investigation

Canadian cybersecurity executive arrested on extortion-related charges

Security Affairs launches weekly AI and cybersecurity newsletter
Anthropic offers free AI vulnerability scans to open-source projects

FBI arrests another suspect linked to ShinyHunters jobs-site breach
AI agents push identity security to the forefront for companies
AnyDesk Linux flaw allowed attackers to gain root access without approval
Attackers exploit AhsayCBS flaws to install webshells and crypto miners

Organizations urged to prepare for quantum-resistant encryption

Allied alert details cyber tactics linked to sanctioned Chinese group
AI-assisted attacks hit South Korean financial institutions
