Science & Tech · Cybersecurity · 9 hrs ago
CyberXero campaign steals more than 628,000 records tied to Ukrainians

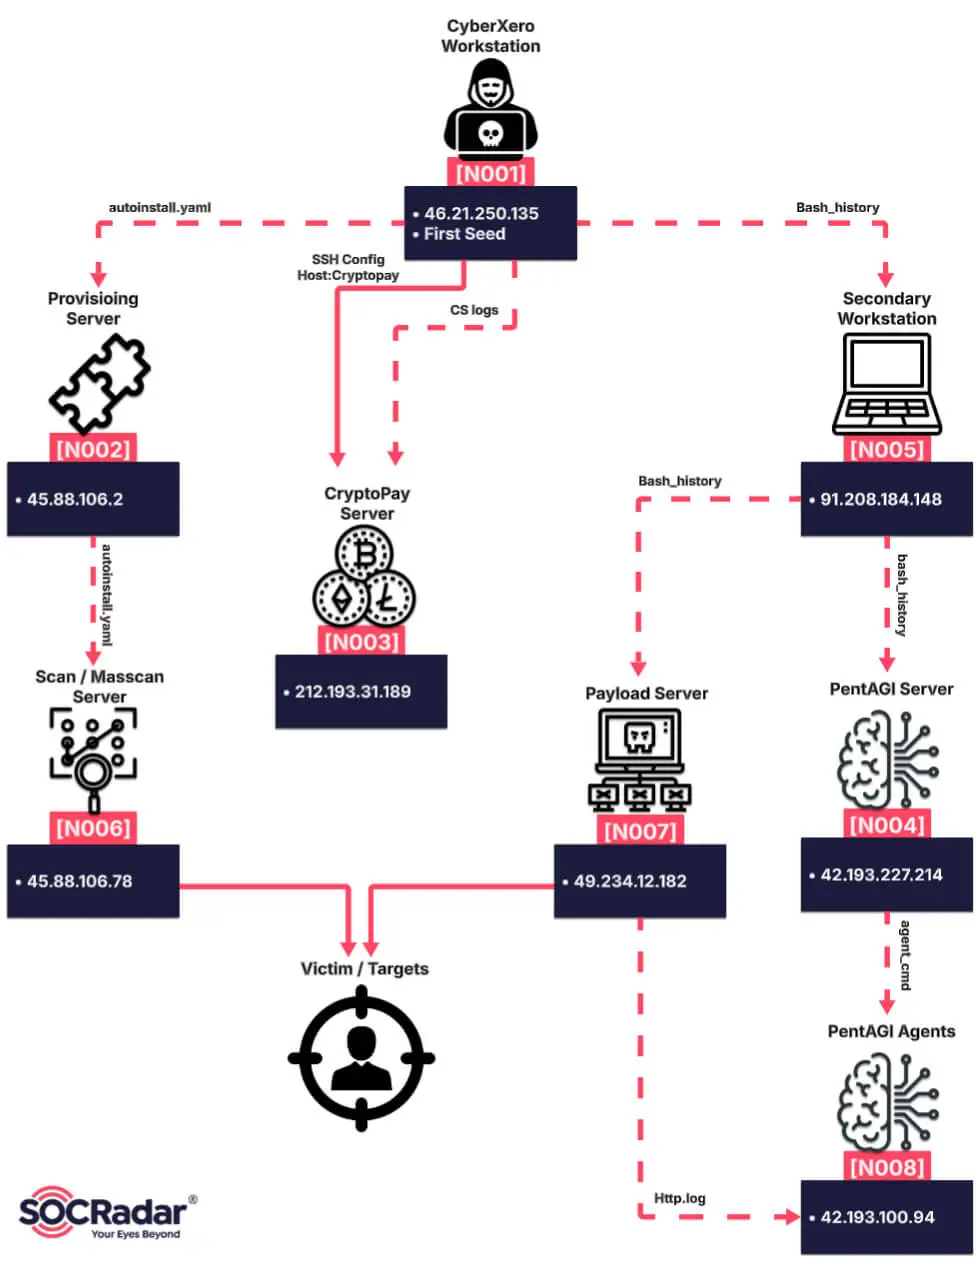
CyberXero is a financially motivated hacking operation that researchers say has used AI tools alongside conventional cyberattack software.
It ran two campaigns: automated attacks on WordPress and online shopping sites worldwide, and targeted attacks on energy and utility organizations in Ukraine.
Researchers say the operation stole more than 628,000 records tied to Ukrainian individuals from four Ukrainian organizations.
One case involved a heating provider in Kharkiv, where more than 564,000 customer records, including addresses and account numbers, were taken.
Kharkiv is near the front line, so linking people to their home addresses could create risks beyond the loss of privacy.
Researchers found evidence of the operation after an unprotected server exposed its working files, including AI session logs and stolen data.
The campaign is ongoing, and organizations using WordPress, Magento, PrestaShop or internet-facing Redis are advised to check for signs of compromise.

CyberXero stole more than 628,000 records tied to Ukrainian individuals, researchers said.
The Russian-speaking, financially motivated threat actor ran global automated attacks and a separate targeted campaign against Ukrainian energy and utility organizations.
Researchers said CyberXero used AI tools, including Claude Code and a cluster of 51 specialized agents, alongside conventional hacking tools.
An exposed server directory revealed the operation’s working files, AI session logs, scripts and stolen data.
The campaign remains ongoing, and researchers warned that data from Kharkiv could pose physical risks to identifiable civilians.
- Who
- CyberXero, a Russian-speaking, financially motivated initial access broker.
- What
- A two-pronged cyber campaign stole more than 628,000 records tied to Ukrainian individuals and attacked websites and infrastructure.
- When
- The actor was assessed to be active since at least July 2026. The campaign remains ongoing.
- Where
- Globally, including WordPress and e-commerce sites, and at Ukrainian energy and utility organizations.
- Why
- The global campaign sought access and payment data; CyberXero is described as financially motivated. Further motives are not stated.
This story does not have two clearly opposing sides.
The operation runs two pipelines at once: a global, automated campaign against WordPress and e-commerce platforms, and a curated, manual campaign against Ukrainian energy and critical infrastructure
Because Kharkiv sits on an active conflict front, this dataset poses a potential physical risk to identifiable civilians that goes well beyond a conventional data breach.
When an agent refused a task, the actor reopened a fresh session, with the authorization framing preloaded and tried again.
CyberXero was assessed to have been active since at least this month.
Security Affairs and The Hacker News published reports detailing the campaign.
- Records
- More than 628,000 tied to Ukrainian individuals
- AI agents
- 51 specialized agents reported
- Ukrainian organizations
- Four with confirmed data theft
- Automated scan
- 4,708 targets scanned in one execution
- WordPress access
- 429 administration panels accessed
- Web shells
- 32 deployed within 61 seconds
Sources
Related news

Cyberattack defrosts refrigerators at French supermarket chains

Ledger confirms tampered wallets linked to CryptoBilis fund thefts

Malware incident at contractor may expose 8.7 million karaoke records

Critical SonicWall flaw faces exploitation days after patch
Cyberattack disrupts refrigeration systems at French supermarkets

Canadian cybersecurity executive arrested on federal extortion charges
Albert Heijn systems remain offline after cybersecurity incident
Attacks disrupt Yandex services and its data centers in Russia

Canadian cybersecurity executive arrested in FBI ShinyHunters investigation
Cyberattacks disrupt French supermarket freezers and Dutch-Belgian retail operations
Exposure management shifts cybersecurity focus from controls to risk