

Science & Tech · Cybersecurity · 3 hrs ago
Flock gains authority to assign vulnerability IDs for its own products
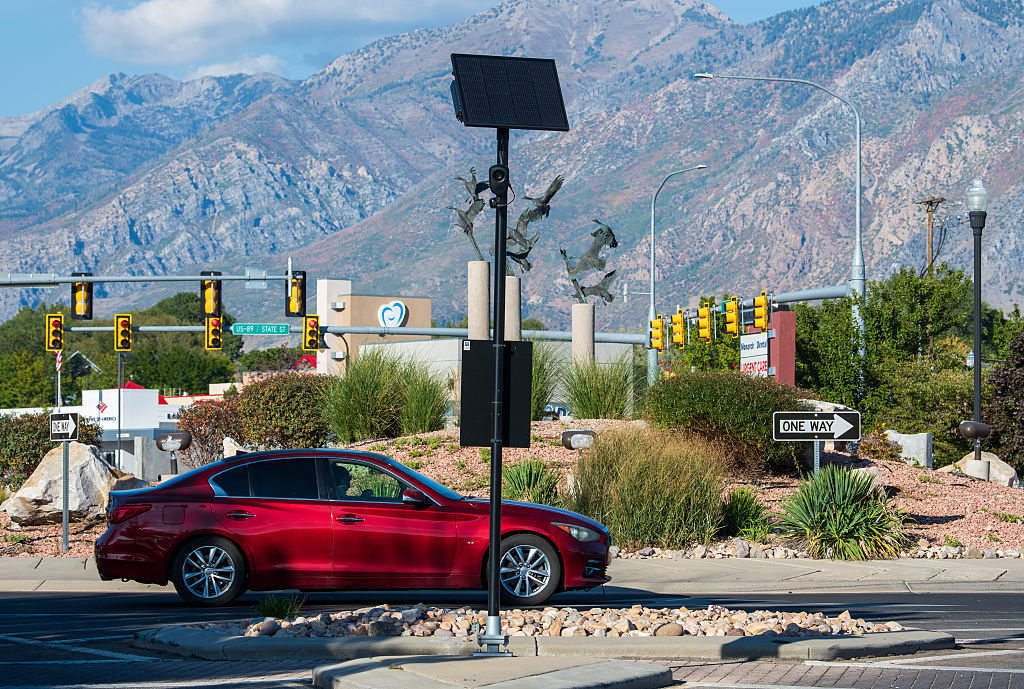
Flock, a public safety company that makes license-plate readers and AI-powered cameras, can now assign CVE IDs to vulnerabilities in its own products.
CVE IDs help identify and track security flaws, and Flock can also assess their severity as a CVE Numbering Authority.
The company says this will help it respond faster and give customers one place to find security information.
Flock has faced privacy concerns and reports of police misusing its technology, which may affect how researchers and the public judge its work.
Security experts say vendors can be well placed to assess flaws in their own products, but they must publish accurate details about affected versions and fixes.
Flock's disclosure policy restricts some testing, and the company has no paid bug bounty program.
It has created a security advisories page for newly discovered and confirmed vulnerabilities, while some researchers may continue to disclose flaws without coordinating with the company.

Flock has gained authority to assign CVE IDs and assess vulnerabilities in its own products as a CVE Numbering Authority.
The company says the role will help it respond faster to researchers and provide customers with a single source of security information.
Security experts say vendors can be well placed to assess their own products, but must maintain accurate records and earn trust.
Flock has faced privacy concerns and reports of police misuse of its surveillance products, raising questions about its credibility as a CNA.
Its vulnerability disclosure policy limits some forms of testing and allows it to delay publication if it considers disclosure a safety risk.
- Who
- Flock, a public safety technology company, has become a CVE Numbering Authority for its own products.
- What
- It can assign CVE IDs to vulnerabilities in its products and assess those defects.
- When
- The change was reported on October 12, 2026.
- Where
- Not stated.
- Why
- Flock says the authority will help it respond faster to researchers, avoid duplicate or conflicting entries, and give customers a single source of security information.
Flock
Security experts and critics
Value of CNA authority
Flock
Flock says the role can speed responses to researchers and reduce confusion in vulnerability records.
Security experts and critics
Experts say vendor CNAs can be useful, but credibility depends on accurate records and sound assessment of defects.
Trust and oversight
Flock
Flock says it will publish newly discovered and confirmed vulnerabilities on its security advisories page.
Security experts and critics
Experts raise concerns about conflicts of interest, Flock’s record of public scrutiny, and its policy allowing it to withhold publication for safety reasons.
Researchers reported multiple defects in Flock’s license-plate reader and gunshot detection system.
Flock published its vulnerability disclosure policy.
Flock created a security advisories page for newly discovered and confirmed vulnerabilities.
CyberScoop reported that Flock had gained authority to assign CVE IDs for its own products.
- CNA authority
- Flock can assign CVE IDs to vulnerabilities in its own products
- CNA network
- More than 550 CNAs globally
- Products
- Automated license plate readers and AI-powered cameras
- Vulnerability disclosure policy
- Published in August
- Bug bounty
- Flock does not run a paid bug bounty program
What people are saying
It allows us to move faster when researchers report findings, eliminate confusion from duplicate or conflicting vulnerability entries and give our customers a single, trusted source for security information about our products
The measure of Flock as a CNA is whether its records give cities, police departments, and the public enough detail and accuracy to let people track specific risks by product version, the nature of the vulnerability, and ideally how to mitigate or fix it
essentially grading their own homework
These cameras sit on poles on public streets
Sources
Related news

Cyberattack defrosts refrigerators at hundreds of French supermarkets

Canadian cybersecurity executive arrested on federal extortion charges

Attackers target critical SonicWall SMA 1000 flaw days after disclosure
Data on 3,615 Trump Mobile customers published by hackers
Cyberattack damages refrigeration systems at hundreds of French supermarkets
Five South Korean cybersecurity staff disciplined for accessing StarCraft servers
Hackers take over Brazil’s Ancine website with political messages

Malware incident at contractor may expose 8.7 million karaoke records

Ledger confirms tampered wallets linked to CryptoBilis fund thefts

Canadian cybersecurity executive arrested in FBI ShinyHunters investigation
DDoS attack disrupts Canonical websites for more than four hours
