1 day ago
Congress Websites Exposed Student and Member Data, Researcher Says
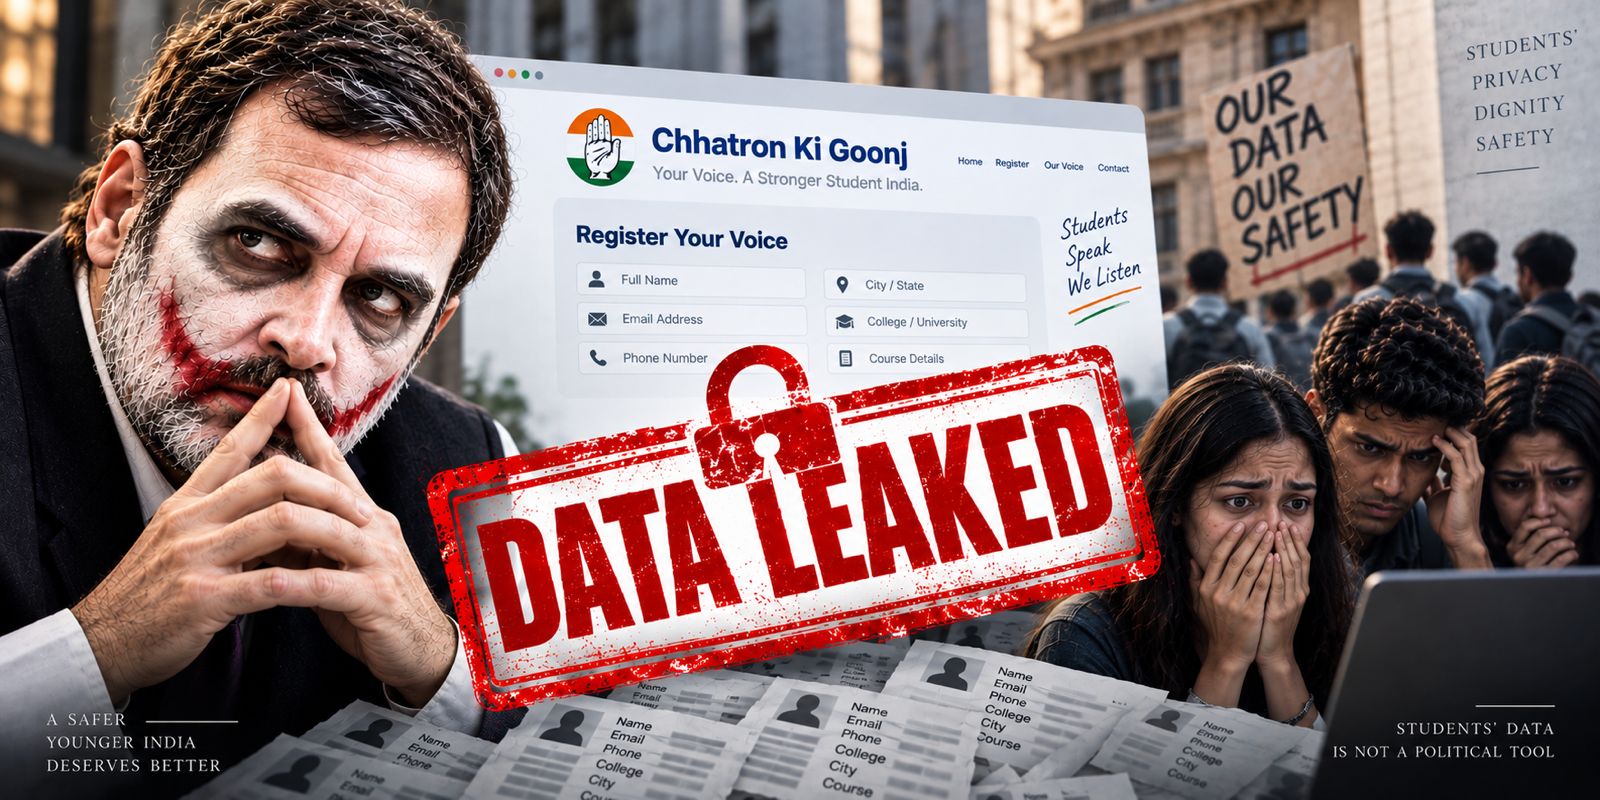
Rahul Gandhi’s Chhatron Ki Goonj campaign asked students to register online.
The form requested information such as names, phone numbers and gender.
A security researcher said the website did not properly protect many registration records.
He said people with technical knowledge could access the records without breaking into an account.
He also found similar problems on a Mahila Congress website.
These exposed details could potentially be used by scammers to contact or trick people.
The researcher said he warned Congress and later contacted India’s computer emergency agency.
Congress eventually said it had fixed the problems, but the researcher said there was no formal public confirmation that the matter was closed.

A registration form for Rahul Gandhi’s Chhatron Ki Goonj campaign was hosted on rahulgandhi.in and collected students’ personal information.
Security researcher Shashi said at least 156,439 student records could be accessed through a publicly discoverable registration endpoint.
He also reported vulnerabilities on the Mahila Congress website, including exposed user details, profile pictures and recruitment links.
Shashi said he first alerted Congress, then contacted CERT-In after receiving no official response for more than a week.
Congress later said its tech team had fixed the issues, but the researcher said he had not received formal closure communication from CERT-In.
- Who
- Students registering for Chhatron Ki Goonj, Congress-affiliated website users, security researcher Shashi, the Congress party and CERT-In.
- What
- A researcher reported that personal data on Rahul Gandhi’s and Mahila Congress websites could be accessed because of cybersecurity vulnerabilities.
- Where
- On rahulgandhi.in and the Mahila Congress website.
- When
- The vulnerabilities were reported after being identified more than a month before the researcher’s blog post; the article cites a September 20, 2026 post and says Congress later claimed the issues were fixed.
- Why
- The researcher said publicly accessible website code, scripts, API calls and endpoints allowed records and other user information to be retrieved without normal authentication.
Security Researcher’s Concerns
Congress’s Response
Extent of exposure
Security Researcher’s Concerns
Shashi said at least 156,439 student records on Rahul Gandhi’s website could be retrieved at scale and reported additional vulnerabilities on the Mahila Congress website.
Congress’s Response
Congress’s reported response was that the website issues had been fixed after its technology team contacted the researcher.
Handling of the warning
Security Researcher’s Concerns
Shashi said he initially alerted Congress, waited more than a week without an official response, and then contacted CERT-In.
Congress’s Response
Website vendors reportedly told the researcher that Congress authorities had been informed, and CERT-In later communicated with the affected party.
Public disclosure
Security Researcher’s Concerns
The researcher said Congress had not publicly acknowledged the potential exposure or formally confirmed closure through CERT-In.
Congress’s Response
Congress disabled several information- and donation-collection pages and later said the vulnerabilities had been resolved.
Key facts
- Campaign
- Chhatron Ki Goonj
- Registration website
- rahulgandhi.in
- Student records reportedly exposed
- At least 156,439, according to researcher Shashi
- Other affected platform
- Mahila Congress website
- Reported access method
- Publicly observable codes, scripts, API calls and a registration endpoint
- Agency contacted
- Indian Computer Emergency Response Team (CERT-In)
- Congress response
- The party later told the researcher that the issues had been fixed
Sources
Related news
Congress Websites Reportedly Redirected Youth to Betting Platforms
Website Flags 29 of 40 Rahul Gandhi Claims as False
Rahul Gandhi Alleges Ajit Doval Controls Indians’ Communications
Congress Accuses Madhya Pradesh Government of Blocking Student Event
Posters Target Rahul Gandhi Ahead of Indore Student Event
Uttar Pradesh MLAs Get Cybersecurity Advice After Viral Fake Posts
Rahul Gandhi Indore Visit Sparks Congress-BJP Clash Over Remarks
Amit Shah to Lead National Conference on Drug Control
Uttar Pradesh Minister Claims State Will Split Into Four
China’s Tactical India Rapprochement Is Shaped by US Ties
BJP Leader Demands Rahul Gandhi Apology Over Mother Remarks