

Science & Tech · Cybersecurity · 2 hrs ago
Rakuten Travel says customer data was accessed in two security incidents
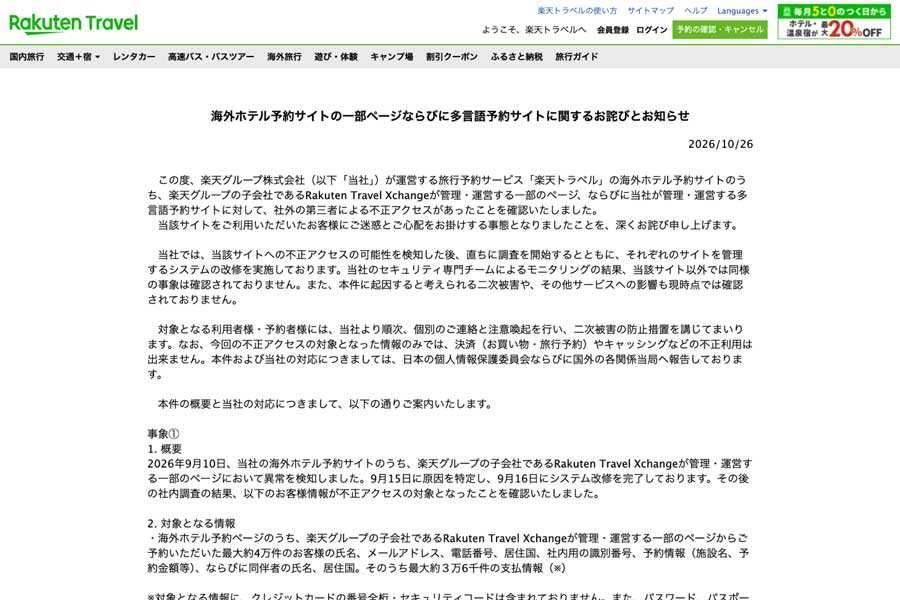
Rakuten Group said customer data was accessed on two Rakuten Travel booking sites.
One incident involved pages run by its Singapore subsidiary for overseas hotel bookings, and the other involved its multilingual booking site.
Up to 2.6 million users’ details were affected on the overseas hotel site, while up to 860,000 users’ email addresses and internal IDs were affected on the multilingual site.
For up to 36,000 users, payment details included the cardholder name, expiry date, card brand, issuer identifier and last four digits, but not the full card number or security code.
The exposed details alone cannot be used to make payments, and the company says it has not found other harm or effects on its other services.
Rakuten says it blocked access and fixed the systems, and will contact affected users; it has reported the incidents to data protection authorities.

Rakuten Group said customer data on two Rakuten Travel booking sites was accessed without authorization.
The first incident involved up to about 2.6 million users of some pages on its overseas hotel booking site.
Reservation details for up to about 40,000 people may also have been accessed, including payment information for up to about 36,000.
A second incident affected the multilingual booking site, where email addresses and internal identification numbers for up to about 860,000 users may have been accessed.
Rakuten said it blocked the access routes, updated the systems and had not confirmed secondary harm or effects on other services.
- Who
- Rakuten Group, which operates the Rakuten Travel booking service, reported the incidents.
- What
- Unauthorized access affected data on two Rakuten Travel sites. Some payment information may have been accessed, but full card numbers and security codes were not included.
- When
- The incidents were detected on September 10 and October 20. Rakuten announced them on October 26, 2026.
- Where
- Some pages of an overseas hotel booking site operated by Rakuten’s Singapore subsidiary, and its multilingual booking site.
- Why
- Not stated
This story does not have two clearly opposing sides.
Rakuten detected an anomaly on some pages of the overseas hotel booking site.
Rakuten identified the cause of the first incident.
Rakuten completed system updates for the affected overseas hotel booking pages.
Rakuten detected possible unauthorized access to the multilingual booking site.
Rakuten completed system updates for the multilingual booking site.
Rakuten Group announced the two incidents.
- Affected service
- Rakuten Travel
- First incident: logged users
- Up to about 2.6 million
- First incident: reservation information
- Up to about 40,000 people
- First incident: payment information
- Up to about 36,000 people
- Second incident: user email addresses
- Up to about 860,000 users
- Second incident: affected operator
- Rakuten Travel Xchange, a Singapore subsidiary
3 sources
What people are saying
The information subject to unauthorized access alone cannot be used for unauthorized payments (shopping or travel bookings) or cash withdrawals.