

Science & Tech · Cybersecurity · 1 hr ago
Old Broadcom Wi-Fi flaw lets attackers take control of some routers
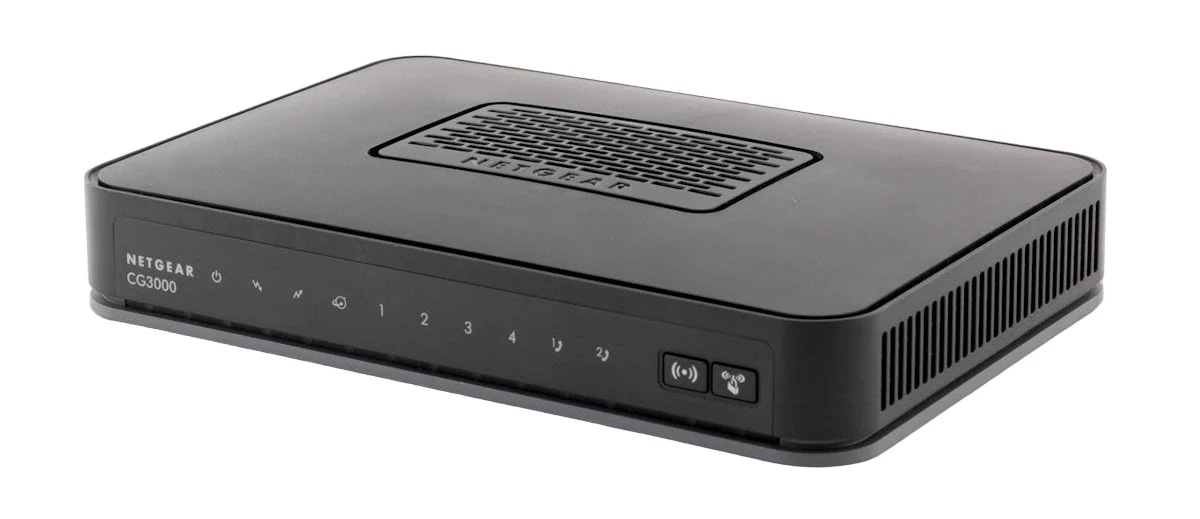
A Broadcom Wi-Fi flaw dating back to 2010 can let attackers run code on some routers without a password.
The weakness is in Broadcom software used by routers to handle part of the wireless setup process.
An attacker only needs to be within Wi-Fi range; no user action or completed setup is required.
Researcher Quentin Kaiser demonstrated the attack on an Orange Belgium ASKEY TCG3000 and a Proximus Sagemcom F@st/BBOX3V+ router, extracting a Wi-Fi password from one device and opening a remote shell on the other.
The flaw can expose passwords and give attackers control of vulnerable routers, putting connected networks at risk.
Broadcom released an incomplete fix in 2018, and Kaiser said affected devices in Belgium had not received a patch by October 15, 2026.
Some affected devices may remain vulnerable: fixing others depends on whether their manufacturers act, and the sources describe no broader patch plan.

A Broadcom Wi-Fi flaw dating back to at least 2010 can let attackers within Wi-Fi range run code on some vulnerable routers without authentication.
Researcher Quentin Kaiser demonstrated working exploits against two routers used in Belgium.
The flaw can expose information, including a router’s Wi-Fi password, and give an attacker control to run code.
Security Affairs reported that as of October 15, 2026, none of the affected devices in Belgium had received a patch.
Broadcom released an incomplete fix in 2018 and later told Kaiser a patch was available, directing him to ask device manufacturers to contact the company.
- Who
- Attackers within Wi-Fi range can exploit the flaw. Researcher Quentin Kaiser documented and demonstrated it.
- What
- A flaw in Broadcom’s proprietary Wi-Fi implementation can allow unauthenticated code execution on vulnerable routers.
- When
- The flaw has been present since at least 2010. Kaiser reported it to Broadcom in July 2026.
- Where
- The affected routers include devices used in Belgium; Kaiser presented his research at Hexacon in Paris.
- Why
- The flaw is in the WPS EAP reassembly code. The sources do not state why the vulnerability was originally introduced.
This story does not have two clearly opposing sides.
The vulnerability was present in Broadcom’s software development kit.
Broadcom released an incomplete fix, according to Kaiser.
Kaiser reported the bugs to Broadcom.
Security Affairs reported that none of the affected devices in Belgium had received a patch.
Security Affairs published its report on the vulnerability.
- Affected software
- Broadcom proprietary 802.11 implementation
- Vulnerability area
- WPS EAP reassembly code
- Demonstrated router
- Orange Belgium ASKEY TCG3000
- Demonstrated router
- Proximus Sagemcom F@st/BBOX3V+
- eCos chipsets cited
- BCM3380, BCM3383, BCM33834
- Linux chipsets cited
- BCM3390, BCM65xx, BCM68xx
What people are saying
The vulnerability can be triggered remotely over WiFi without knowledge of the network key or completion of a normal WPS enrollment. Exploitation provides controlled information disclosure and arbitrary code execution.
A vulnerability affecting Broadcom’s proprietary implementation of 802.11 has been present in their SDK since at least 2010. An incomplete patch was silently released in 2018, followed by Broadcom’s recommendation to move to hostapd instead, making it a definitive forever day on eCos-based platforms (BCM3380, BCM3383, BCM33834) and a potential forever day on Linux platforms (BCM3390, BCM65xx, BCM68xx) unless affected Original Equipment Manufacturers (OEMs) are willing to migrate.