

Science & Tech · Cybersecurity · 7 hrs ago
GETTIIS ticket service confirms member data leak after cyberattack
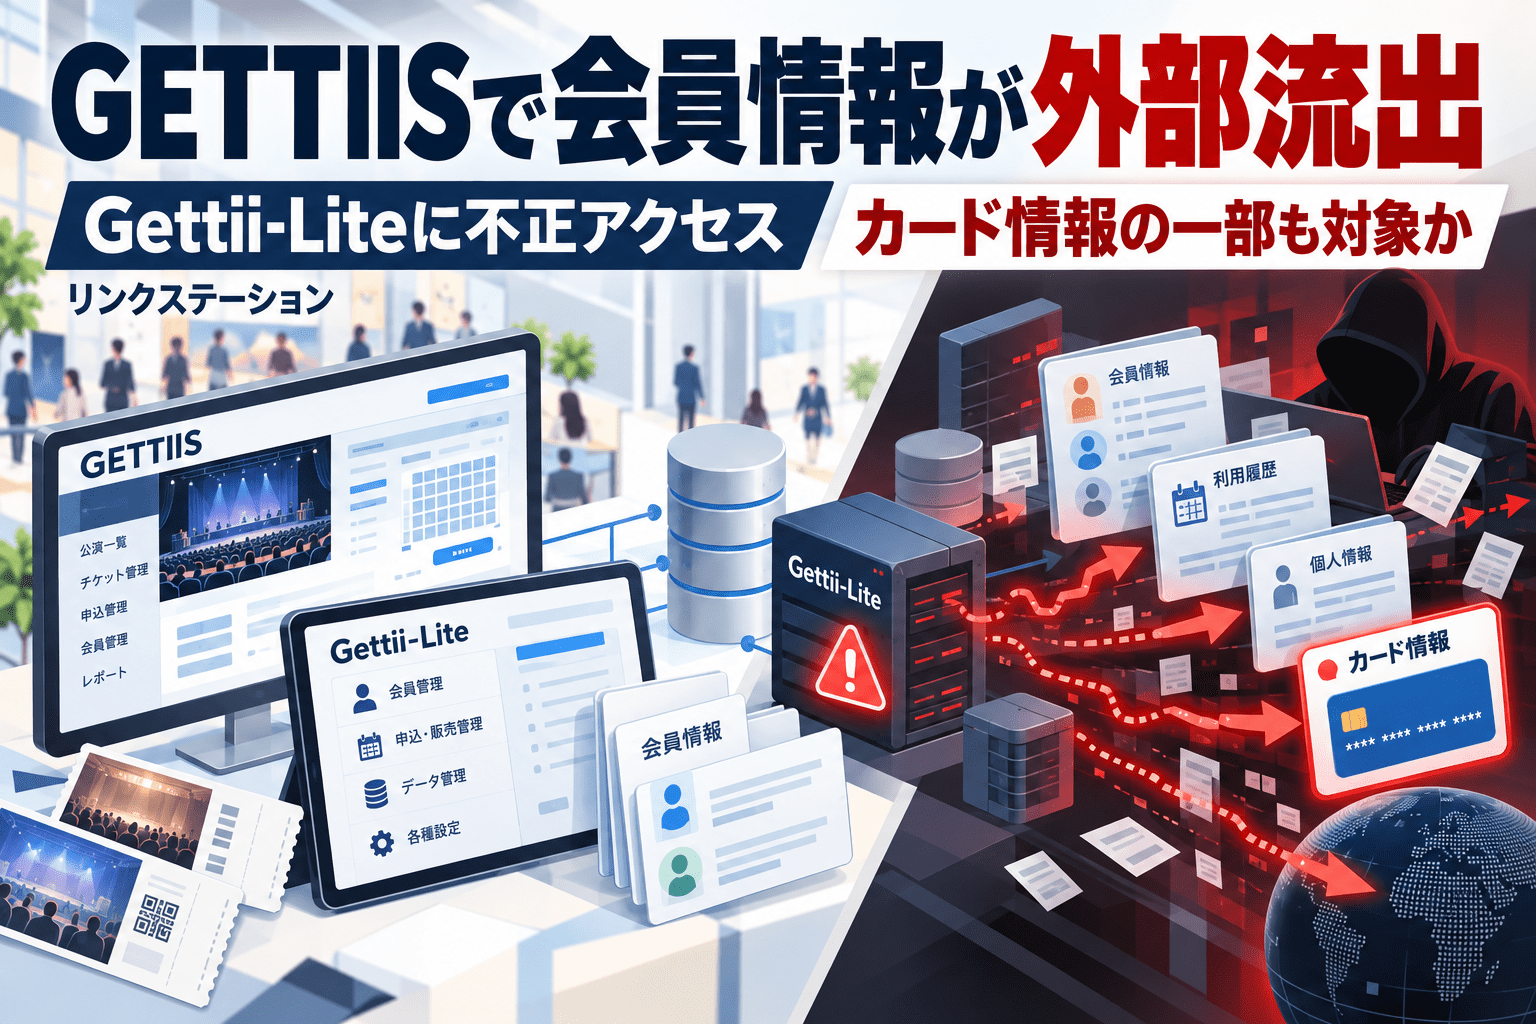
Japan-based Link Station confirmed GETTIIS member data was exposed after an unauthorized access incident.
Attackers exploited a weakness in Gettii-Lite, a service used by event organizers, while the exposed information belonged to customers of GETTIIS, the ticket-buying service.
Potentially affected details include names, contact information, dates of birth, hashed passwords and some encrypted card information.
The company says it did not store full card numbers or security codes, and the exposed data alone cannot be used to make card payments.
The number of affected members and the exact data exposed are still being checked.
Link Station says it has moved the affected server and fixed the weakness, and will contact affected users individually.
It is asking GETTIIS users to change their passwords, change reused passwords on other services, and watch for suspicious messages or calls.

Link Station said on October 19 that member information from its GETTIIS ticket-purchasing service had leaked after a cyberattack.
The company said an attacker exploited a vulnerability in the server for Gettii-Lite, a service for event organizers.
Information that may have been affected includes names, contact details, dates of birth, hashed passwords and some credit card data.
The number of affected members and the specific information exposed for each person are still being investigated.
Link Station said it had switched the affected server, addressed the vulnerability and would contact affected users individually.
- Who
- Link Station, the Aomori City company that operates GETTIIS.
- What
- The company confirmed that GETTIIS member information had leaked after an unauthorized access incident.
- When
- The intrusion was identified on October 18, 2026, and Link Station announced the leak on October 19.
- Where
- The attack exploited a vulnerability in the server for Gettii-Lite. The leaked information was from the GETTIIS ticket-purchasing service.
- Why
- A third party exploited a vulnerability in the Gettii-Lite program.
This story does not have two clearly opposing sides.
Link Station identified suspicious access and found that a third party may have exploited a Gettii-Lite vulnerability to obtain GETTIIS member information.
Link Station announced that GETTIIS member information had leaked and said it was investigating the affected records and number of members.
- Operator
- Link Station, based in Aomori City
- Affected service
- GETTIIS, the ticket-purchasing service
- Compromised server
- Gettii-Lite, the event-organizer service
- Possible data
- Member details, hashed passwords and some encrypted credit card information
- Affected members
- Number and individual records under investigation
- Other services
- No impact confirmed for Gettii or Gettii-EC