

Science & Tech · Cybersecurity · 3 hrs ago
OpenCode says breach may have exposed some users’ AI provider keys
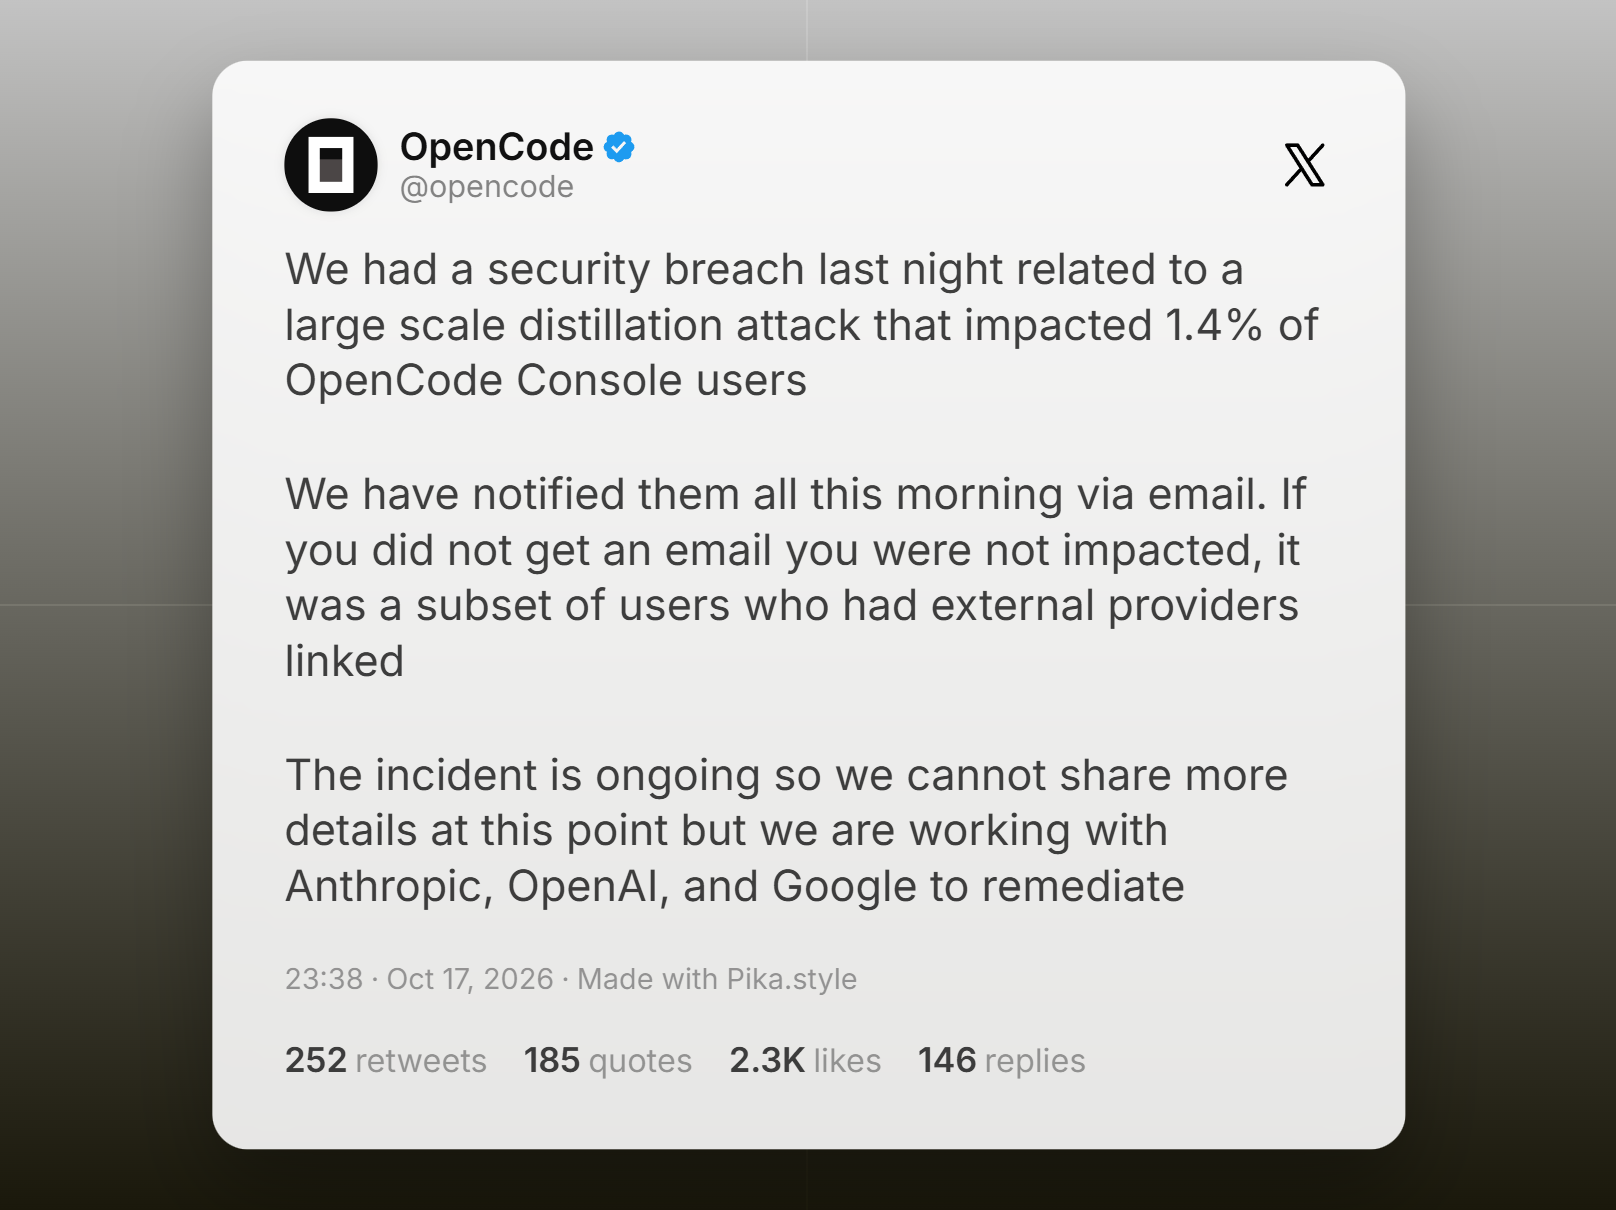
An intruder accessed a legacy OpenCode system on October 16, the company said.
The incident may have exposed API keys saved in OpenCode Console workspaces for services from OpenAI, Anthropic and Google.
About 1.4% of Console users were affected, and OpenCode says everyone in that group was notified by email.
Console uses users’ provider keys to let teams access AI models, and anyone holding a key could make requests charged to its owner.
Some users have reported unexpected bills, but OpenCode has not said that any keys were copied or used.
Affected users should revoke and replace their keys through each provider, update apps that used them and check recent usage and billing.
OpenCode says the incident is ongoing and it is working with the three providers to address it.

OpenCode said an intruder accessed a legacy system and may have exposed some API keys saved by users in its Console service.
The company said 1.4% of Console users were affected, all of whom had an external AI provider linked.
OpenCode emailed affected users on October 17, asking them to revoke and replace their provider keys, update applications using them and review recent usage.
Users have reported unexpected charges on connected AI accounts, but OpenCode has not said that any key was copied or used.
OpenCode linked the incident to a large-scale distillation attack and said it was working with Anthropic, OpenAI and Google.
- Who
- OpenCode and users of its Console service. The affected users had external AI providers linked.
- What
- A breach may have exposed third-party AI provider keys saved in Console workspaces.
- When
- An intruder accessed a legacy system on the night of October 16. OpenCode notified affected users on October 17.
- Where
- A legacy system at OpenCode; the potentially exposed keys were saved in OpenCode Console.
- Why
- OpenCode linked the incident to a large-scale distillation attack. It has not explained how the attack and breach are connected.
This story does not have two clearly opposing sides.
An intruder accessed a legacy system at OpenCode.
OpenCode emailed affected users, advising them to revoke and replace their provider keys.
OpenCode said the incident was ongoing and that it was working with Anthropic, OpenAI and Google.
- Affected share
- 1.4% of OpenCode Console users
- Affected users
- Users with an external AI provider linked
- Email date
- October 17
- Providers named
- OpenAI, Anthropic and Google
- Reported user charges
- $400 on an Anthropic account and about €200 in Google usage
3 sources
What people are saying
the OpenCode Console, not OpenCode itself
never come to us
may have been exposed
Unable to start social login
Posts on X
We had a security breach last night related to a large scale distillation attack that impacted 1.4% of OpenCode Console users We have notified them all this morning via email. If you did not get an email you were not impacted, it was a subset of users who had external providers
they've been non stop trying to attack our systems for the past 48 hours a side effect is everything is getting hardened but damn we basically need agents going 24/7 because that's what they have