

Science & Tech · Cybersecurity · 6 hrs ago
US agencies warn of attacks on industrial refrigeration controllers
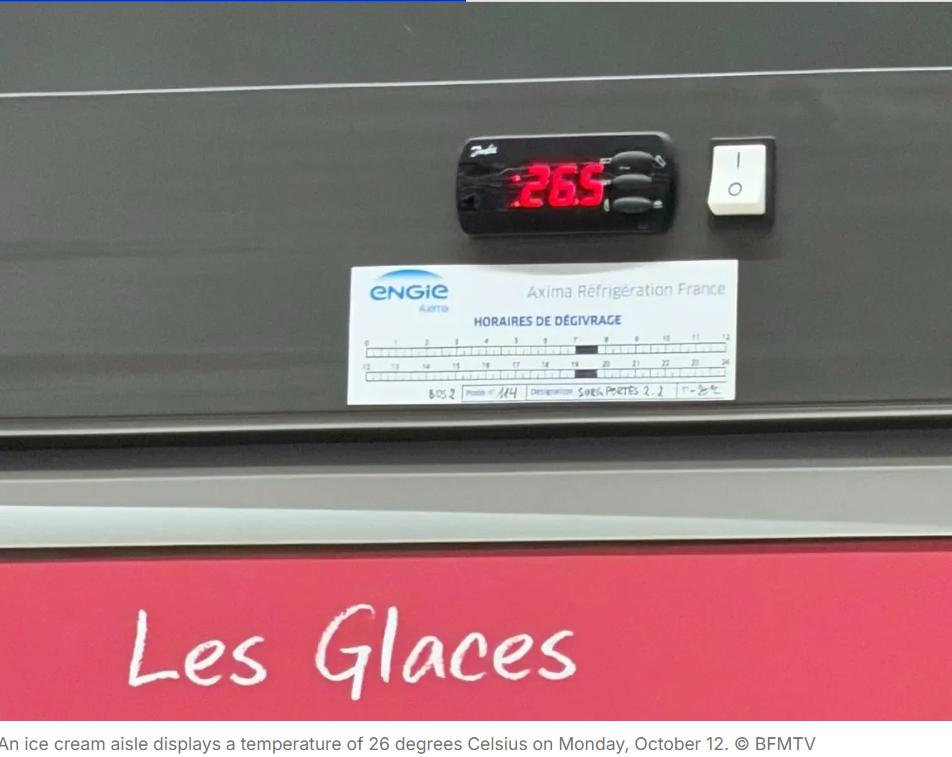
US agencies warn that attackers are targeting industrial refrigeration controllers worldwide.
These systems help grocery stores, cold-storage sites and other businesses monitor temperatures and manage refrigeration equipment.
Attackers may exploit outdated devices, weak settings or internet access to change temperatures remotely.
The changes can spoil stock, damage equipment and create fire or food-safety risks.
The agencies urge operators to keep controllers off the internet where possible, use secure remote access and separate equipment from office networks.
They also recommend changing default passwords, updating firmware, limiting who can change settings and keeping tested backups.
US organizations should report suspicious activity to CISA or the FBI, while healthcare organizations can also contact HHS.

Five US agencies warned that attackers are targeting industrial refrigeration controllers and cold-chain monitoring systems.
The agencies said attackers may exploit unpatched or internet-accessible devices to change settings remotely.
Those changes could force refrigeration units into continuous heating and defrost cycles, causing inventory loss and equipment hazards.
The activity is global and affects systems used by healthcare, chemical, food and transport companies.
The agencies urged operators to secure remote access and apply basic cybersecurity measures.
- Who
- CISA, the FBI, HHS, USDA and the Department of Transportation issued the warning. Attackers are targeting refrigeration controllers.
- What
- The agencies warned of attacks that could let intruders alter refrigeration settings and disrupt equipment.
- When
- The joint advisory was published on November 9, 2026.
- Where
- The activity is global, targeting grocery and cold-storage facilities and other organizations using these systems.
- Why
- Attackers may exploit vulnerabilities or weaknesses in unpatched or internet-accessible controllers. The sources do not state their motive.
This story does not have two clearly opposing sides.
This story does not have a timeline yet.
- Issuing agencies
- CISA, FBI, HHS, USDA and the Department of Transportation
- Targeted equipment
- Electronic temperature controllers and commercial refrigeration controllers
- Affected sites
- Retail grocery and cold-storage facilities
- Potential impact
- Inventory loss and equipment hazards
- Threat scope
- Global
What people are saying
The authoring organizations are aware of malicious cyber actors targeting electronic temperature controllers and commercial refrigeration controllers in retail grocery and cold storage facilities.
The authoring organizations strongly urge industrial refrigeration and cold chain monitoring system owners and operators to secure remote access to their OT systems.