

Science & Tech · Cybersecurity · 9 hrs ago
Fake GitHub Security Tools Infect More Than 2,000 PCs
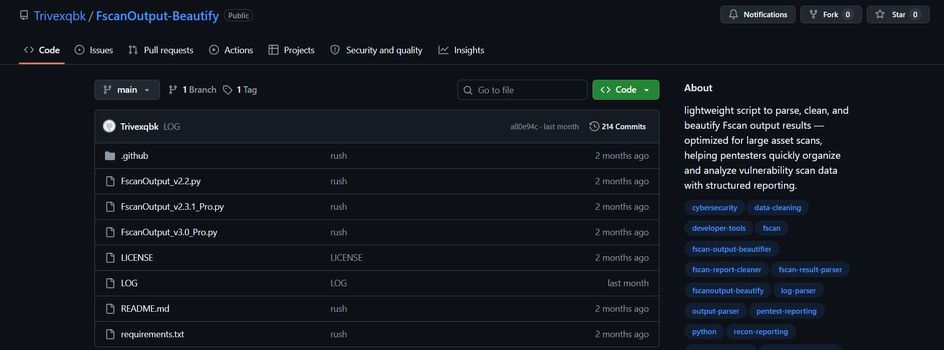
Malware hidden in fake GitHub security tools has infected more than 2,000 PCs, according to cybersecurity firm Doctor Web.
The campaign began two years ago with projects aimed at blockchain game fans and crypto wallet users, and now also targets information security professionals.
The projects claim to offer tools such as automated scanners and security testing software, but opening them can run hidden code on a computer.
The malware can disable Windows protections and remove some antivirus programs, while keeping itself running and hiding its activity.
It can also steal browser and account data, take screenshots, and replace crypto wallet addresses copied to the clipboard.
Stolen information is packaged and sent to the attackers through Telegram, and the malware can block access to antivirus companies’ websites.
Doctor Web found signs the attackers are still developing the malware and advises users to keep antivirus software up to date.

Doctor Web found malware in fake GitHub security projects that has infected more than 2,000 PCs.
The campaign, which began two years ago, first targeted blockchain game fans and has more recently targeted information security professionals.
The malicious software can disable security defenses, remove antivirus products and steal sensitive data.
The attackers’ projects claim to offer tools for automated scanning, security testing and log analysis.
Doctor Web says the attackers are still developing and updating the malware.
- Who
- The attackers behind compromised GitHub projects. Doctor Web discovered the campaign and its malware.
- What
- Fake security tools spread malware that disables defenses, steals data and has infected more than 2,000 PCs.
- When
- The campaign started two years ago. Doctor Web reported its findings on November 9, 2026.
- Where
- The malware was hidden in projects on GitHub and infected PCs. The article does not state where the infected computers were located.
- Why
- The campaign first targeted blockchain game enthusiasts and crypto wallet users, and later targeted information security professionals. The attackers’ motive is not stated.
This story does not have two clearly opposing sides.
The campaign began with Visual Studio projects related to blockchain games, game bots and cheats.
The attackers began targeting information security professionals with fake security tools on GitHub.
Researchers found that more than 2,000 PCs were infected.
Security Affairs published an account of Doctor Web’s findings.
- Infected PCs
- More than 2,000
- First targets
- Blockchain game enthusiasts and crypto wallet users
- New targets
- Information security professionals
- Main malware program
- Microsoft.exe
- Data transfer channel
- Telegram
What people are saying
At the time of Doctor Web’s research into this matter, more than 2,000 PCs were infected.
Attackers are constantly updating the Trojans to introduce new features.