

Science & Tech · Cybersecurity · 1 hr ago
Zyxel fixes zero-day flaw used to hack nearly 1,000 switches
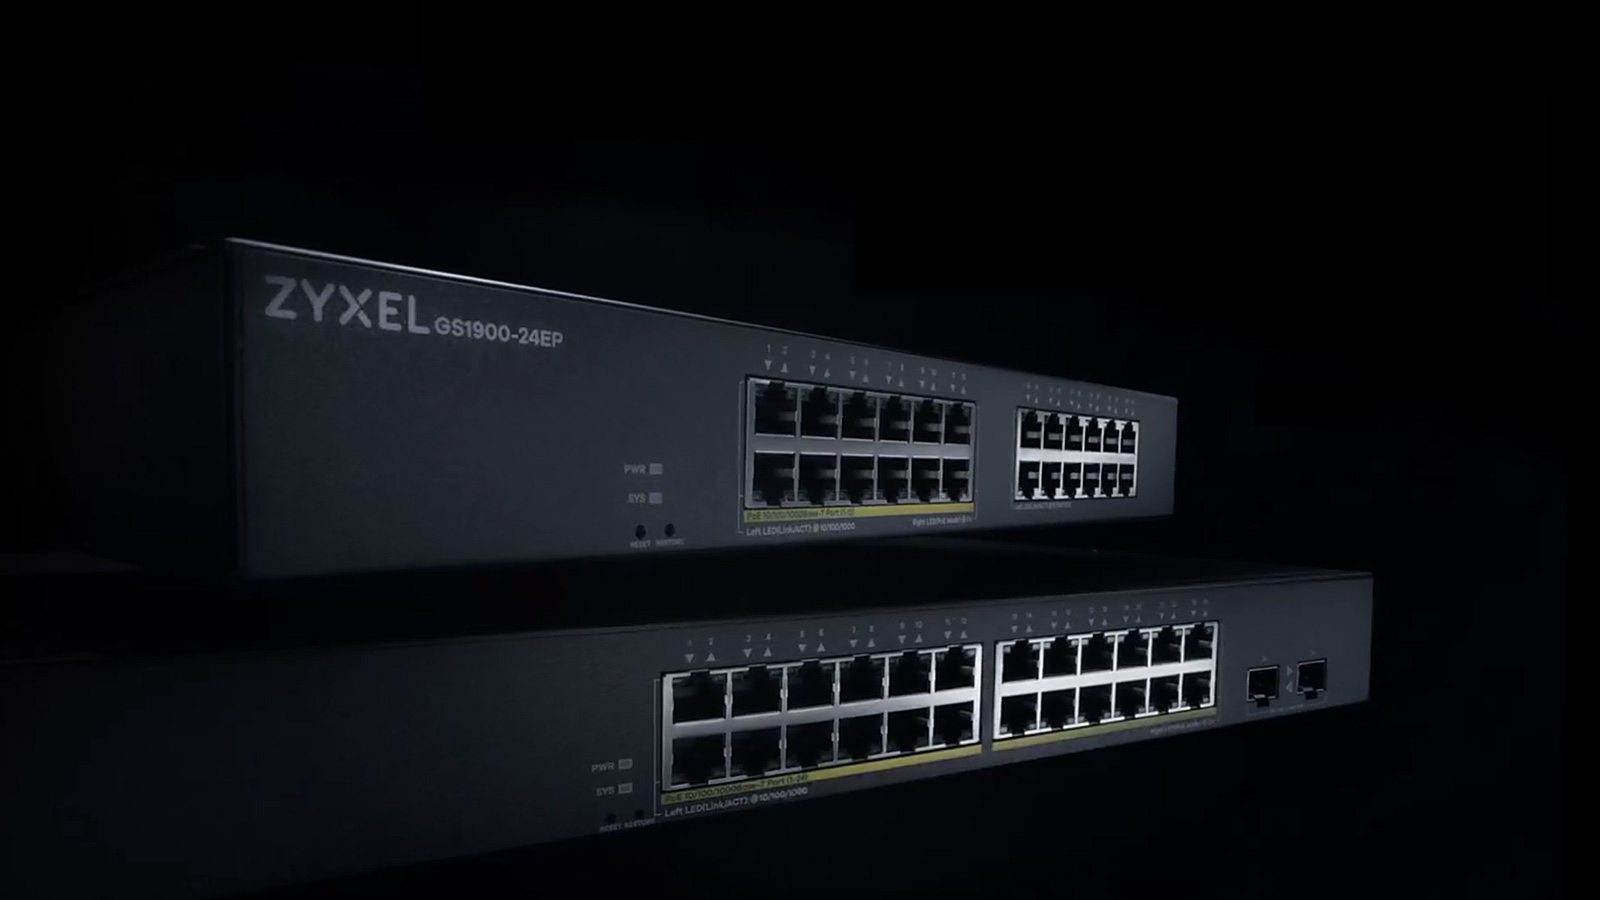
Attackers exploited a previously unknown flaw in Zyxel GS1900 switches to run commands without logging in.
The switches are used to connect devices on networks, and the flaw could be reached through their web management interface by an attacker with network access.
GreyNoise recorded 996 compromised switches across 48 countries in attacks beginning around August 17.
The attackers reportedly took device configurations and hashed root credentials, which can help protect access to a system.
The attacks were first blamed on an older flaw that Zyxel had already patched, but Binarly found the exploit also worked on the patched firmware because a separate weakness remained.
Zyxel has released new firmware for 10 GS1900 models to address the newly identified flaw, CVE-2026-107441.
Administrators should install the latest firmware; the sources do not say whether updates remove access attackers may already have gained.

Zyxel released firmware updates for 10 GS1900 switch models to fix a flaw that can let an unauthenticated attacker with network access run commands.
The flaw, tracked as CVE-2026-107441, remained exploitable even after an earlier update intended to address a different vulnerability.
GreyNoise reported that attackers compromised 996 GS1900 switches in 48 countries, taking configuration data and hashed root credentials.
The attacks were initially linked to CVE-2026-7273, but Binarly found that the exploit also worked against firmware updated for that flaw.
Sources differ on whether Zyxel released the new updates on October 22 or October 23.
- Who
- Attackers targeted Zyxel GS1900 switches; Binarly researchers identified the flaw, and Zyxel released updates.
- What
- Attackers exploited CVE-2026-107441 to run commands and collect data from switches. Zyxel issued firmware updates to fix it.
- When
- Attacks were observed from around August 17, 2026. Zyxel released updates on October 22, according to BleepingComputer, and October 23, according to The Hacker News.
- Where
- The affected devices were Zyxel GS1900 switches. GreyNoise reported compromised devices in 48 countries.
- Why
- The flaw let unauthenticated attackers with network access exploit the switches’ web management interface to run commands.
This story does not have two clearly opposing sides.
Zyxel released updates for CVE-2026-7273, an earlier flaw affecting GS1900 switches.
GreyNoise observed attacks that compromised 996 switches, according to its reporting.
GreyNoise disclosed the attacks and linked them to CVE-2026-7273; CISA added that flaw to its Known Exploited Vulnerabilities catalog.
Binarly reported its findings on the separate vulnerability to Zyxel.
Zyxel confirmed the new vulnerability and assigned it CVE-2026-107441.
Zyxel released the firmware updates; sources differ on the release date.
- Affected models
- 10 Zyxel GS1900 models
- New vulnerability
- CVE-2026-107441
- Compromised devices
- 996 switches
- Countries affected
- 48
- Fixed firmware
- 2.90 Patch 3 builds for the affected models
4 sources
What people are saying
an attacker only needs network reachability to the management service
LAN-based, unauthenticated attacker