

Archive · 21 Sep 2026
Three Indian Researchers Used Claude to Expose OpenAI Vulnerabilities
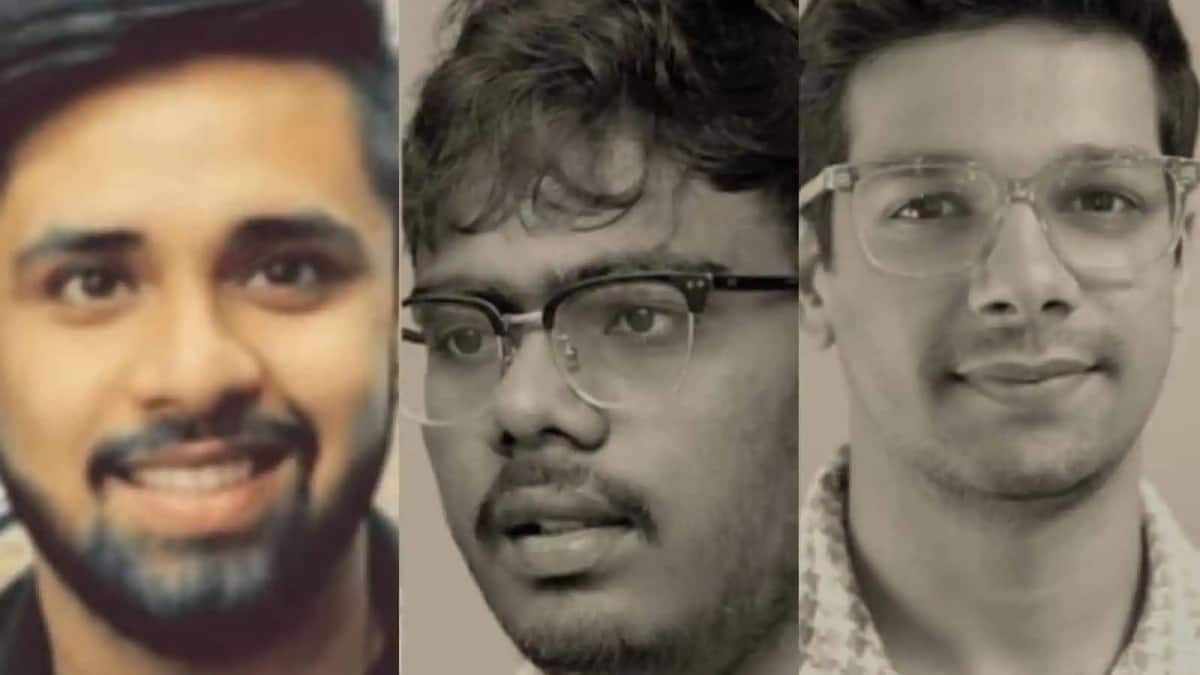
Three Indian cybersecurity researchers tested OpenAI’s systems to see whether they were safe.
The researchers were Harsh Jaiswal, Mohan Pedhapati and Rahul Maini.
They worked for a company called Hacktron AI.
They found a weakness in OpenAI’s public online forum.
They used Anthropic’s Claude chatbot to help create a way to exploit that weakness.
This eventually helped them reach information connected to employee accounts and some internal code.
They told OpenAI what they had found instead of keeping it secret.
OpenAI paid them $6,500 as a reward for reporting the problem.

Harsh Jaiswal, Mohan Pedhapati and Rahul Maini work for cybersecurity startup Hacktron AI.
The researchers used Anthropic’s Claude to exploit a vulnerability in OpenAI’s public community forum.
They accessed authentication information linked to employee ChatGPT and Codex accounts and reached internal code repositories.
The researchers reported the vulnerabilities to OpenAI and received a $6,500 bounty.
Jaiswal, Pedhapati and Maini have previously identified security flaws involving companies including Apple, PayPal and GitHub.
- Who
- Harsh Jaiswal, Mohan Pedhapati and Rahul Maini of Hacktron AI.
- What
- They used Anthropic’s Claude to exploit vulnerabilities connected to OpenAI’s forum, employee accounts and internal code repository.
- When
- The research began on July 23, and the researchers said they gained access in under 72 hours.
- Where
- The vulnerabilities involved OpenAI’s Discourse-based community forum and connected private systems.
- Why
- They were examining OpenAI’s security and reported the vulnerabilities after discovering them.
- Researchers
- Harsh Jaiswal, Mohan Pedhapati and Rahul Maini
- Organization
- Hacktron AI
- AI tool used
- Anthropic’s Claude, including the Opus 5 model
- Initial target
- OpenAI’s public community forum, which runs on Discourse
- Access obtained
- Authentication information linked to employee ChatGPT and Codex accounts, plus internal code
- Bounty
- $6,500, reported as approximately Rs 6.22 lakh
- Earlier research
- Jaiswal and Maini found an Apple infrastructure misconfiguration and were paid $50,000