Science & Tech · Cybersecurity · 5 hrs ago
GitLab patches critical flaw in self-managed server software
GitLab has fixed a critical security flaw in its Community Edition and Enterprise Edition server software.
The vulnerability could have allowed an attacker to run code remotely on an affected server.
It stemmed from the software not checking user input for malicious text.
GitLab urged customers who manage their own installations to upgrade to a newly released version immediately.
The company says its cloud-hosted services are safe because it has already updated its servers.
GitLab is widely used in software development, making its systems a potential target for attackers seeking sensitive information or access to applications before release.
It is not clear whether anyone has exploited this flaw, and the US cybersecurity agency CISA had not listed it as actively exploited as of Monday morning.

GitLab said it fixed a critical vulnerability that could have allowed attackers to execute remote code on affected servers.
The flaw, tracked as CVE-2026-97229, affected GitLab Community Edition and Enterprise Edition self-managed servers.
The company released patched versions of both editions and urged customers to upgrade immediately.
GitLab said cloud-hosted instances were safe because it had upgraded its own servers.
It was unclear whether attackers had begun exploiting the flaw.
- Who
- GitLab disclosed the flaw and released fixes. The vulnerability could have allowed an attacker to execute remote code.
- What
- A critical flaw in GitLab server software was patched.
- When
- GitLab announced the fix on Monday, October 12, 2026.
- Where
- The flaw affected self-managed GitLab Community Edition and Enterprise Edition servers.
- Why
- The servers failed to check user input for malicious text.
This story does not have two clearly opposing sides.
GitLab issued an emergency patch for a flaw that could have let hackers tamper with projects.
CISA warned that hackers were exploiting another GitLab flaw that could have enabled unauthorized file access.
GitLab said it had fixed CVE-2026-97229 and urged customers to upgrade.
- Vulnerability
- CVE-2026-97229
- Severity
- Critical
- Affected products
- GitLab Community Edition and Enterprise Edition servers
- Potential impact
- Remote code execution on an affected server
- Cloud-hosted instances
- GitLab said they were safe because it had upgraded its own servers
What people are saying
These versions contain important bug and security fixes
and we strongly recommend that all self-managed GitLab installations be upgraded to one of these versions immediately.
Sources
Related news

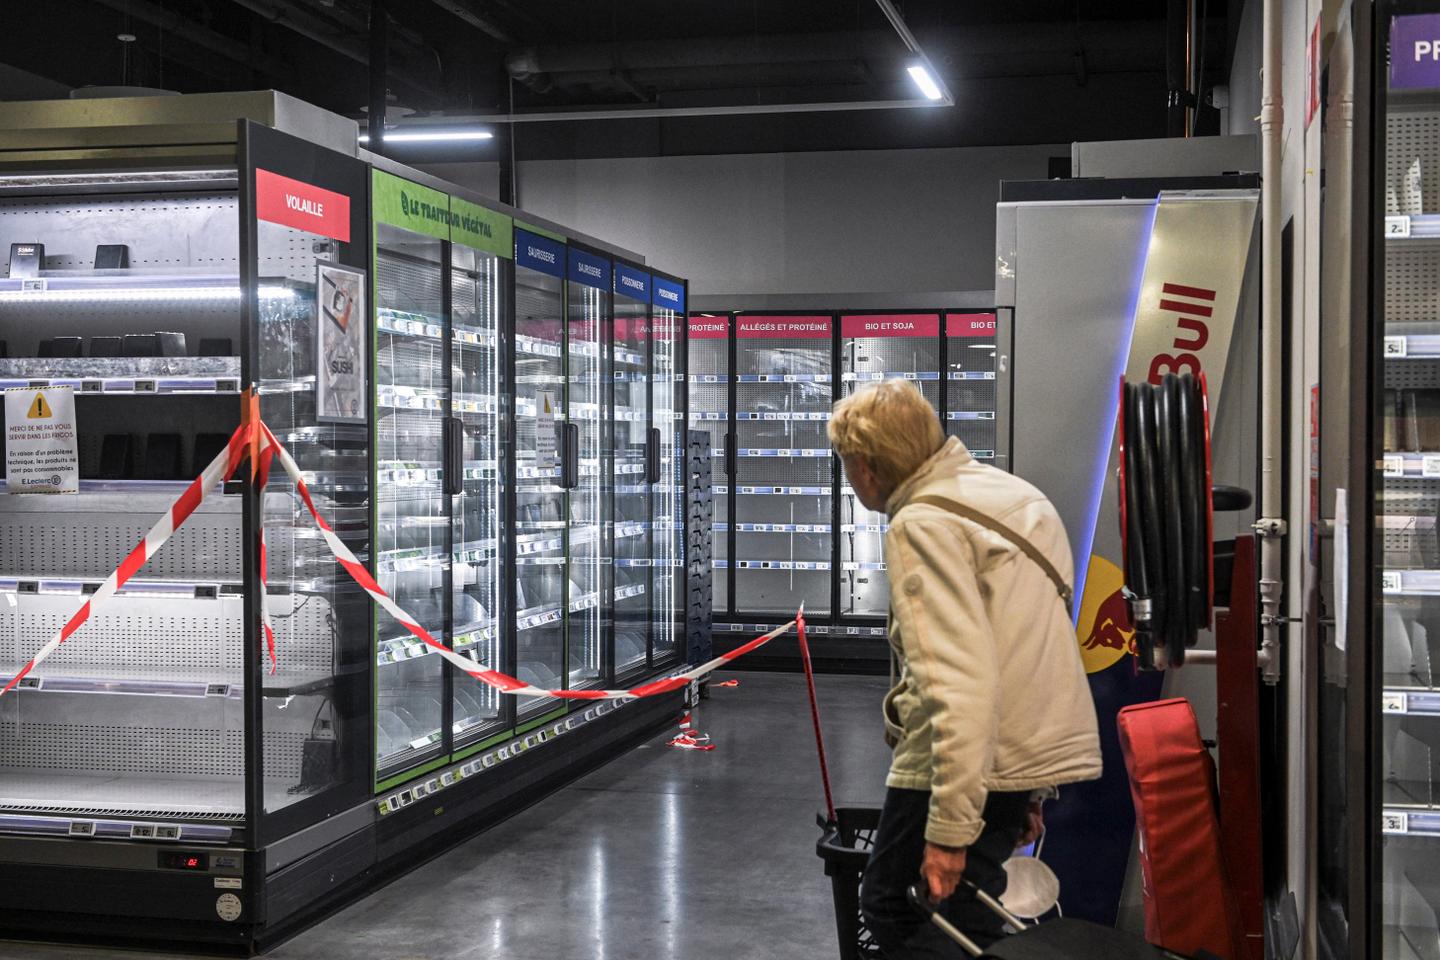
Cyberattack defrosts refrigerators at French supermarket chains

Ledger confirms tampered wallets linked to CryptoBilis fund thefts

Malware incident at contractor may expose 8.7 million karaoke records

Critical SonicWall flaw faces exploitation days after patch

Canadian cybersecurity executive arrested on federal extortion charges

Canadian cybersecurity executive arrested in FBI ShinyHunters investigation
Identity systems are a key part of cyber recovery planning
Pentagon data breach affected more than 3 million people
Cyberattack disrupts refrigeration systems at French supermarkets
Albert Heijn systems remain offline after cybersecurity incident